Laravel MongoDB 5.11: what I would change after CVE-2026-88022
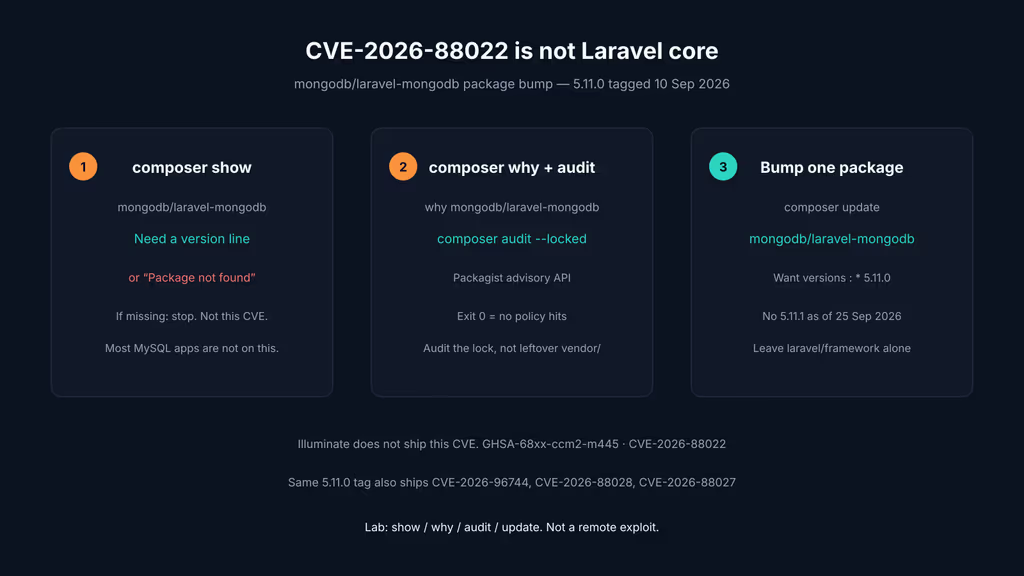
mongodb/laravel-mongodb 5.11.0 tagged 10 Sep 2026 for CVE-2026-88022. A 3-arg where('=', $array) is now a literal $eq. I would run composer show and composer audit --locked before I claim I am patched. This is not a Laravel core CVE.
Sep 25, 2026 · 8 min read