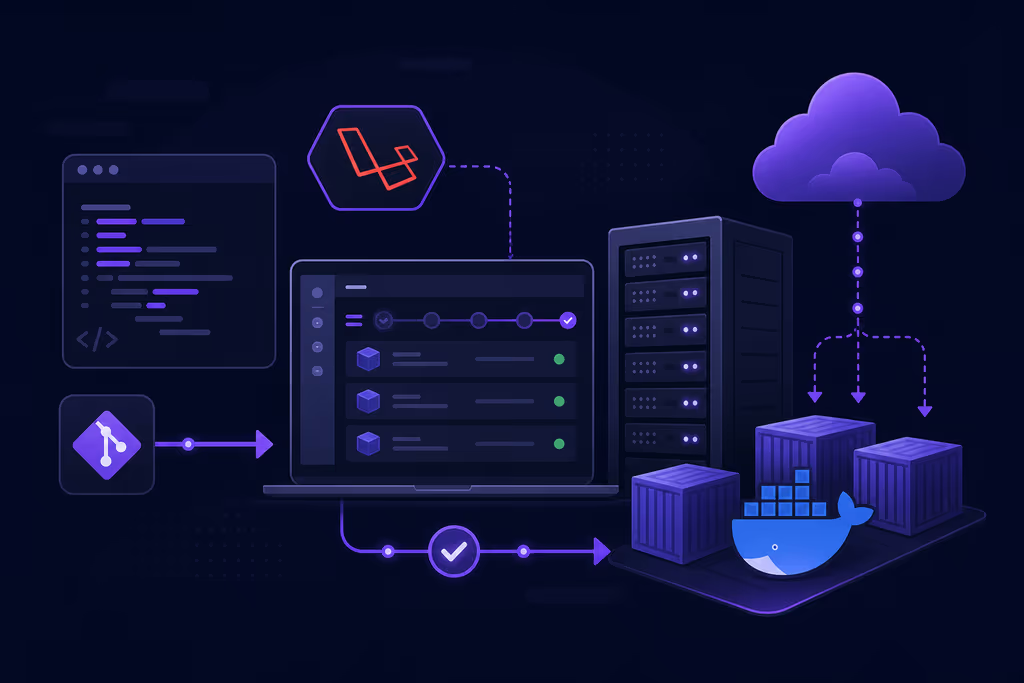
Caption: Coolify on my VPS — a dashboard that deploys apps with Docker instead of a hosted PaaS.
Introduction
I wanted git-push deploys on a VPS I already pay for — not another Heroku, Vercel, or Forge invoice. Coolify looked right: a self-hosted PaaS, one-click databases, and a UI that talks to Docker for me.
On a fresh Ubuntu 24.04 box this install is famous for dying if Docker came from Ubuntu's snap. The official script wants Docker Engine from Docker's apt repo. I hit that wall, purged snap Docker, reran the installer, and the dashboard came up on port 8000.
Coolify v4 is a Node.js + Docker stack. There is no Composer package to install, and I am not going to invent one. The path is still the install script, files under /data/coolify, and Compose. I still deploy Laravel apps onto Coolify — that is usage, not how Coolify itself is built.
Why I picked Coolify
- I keep infrastructure on my own boxes instead of locking into a hosted PaaS.
- Git-based deploys with Nixpacks or Docker match how I already ship.
- One-click Postgres, MySQL, Redis, and a pile of other services save me from hand-writing every Compose file.
- I can add a second server later without changing the mental model.
- The UI shows logs and resource use while a deploy is actually running.
I am not pretending this replaces a full ops team. It replaces the "open five SSH sessions and remember which port I published" part of my week.
Prerequisites
Hardware (minimum):
- CPU: 2 cores
- RAM: 2 GB (4–8 GB if I plan to run several apps)
- Storage: 30 GB free (SSD; more for images and app data)
- 64-bit (AMD64 or ARM64)
What I actually use for production:
- 4+ cores, 8+ GB RAM, 100+ GB storage.
OS: Ubuntu LTS (20.04, 22.04, 24.04) is the path I follow. Other Debian-family, RHEL-family, SUSE, Arch, Alpine, or 64-bit Raspberry Pi OS can work; I have not labbed those here.
Software & accounts:
- A fresh server with root SSH access.
- A domain (optional on day one, required before I trust HTTPS).
- GitHub/GitLab/Bitbucket for the apps I want to deploy.
- Comfortable with Linux, SSH, and Docker.
Security notes:
- I use a fresh server so leftover Docker/snap packages do not fight the installer.
- Firewall on (UFW or firewalld).
- SSH keys; password login off on anything facing the internet.
Installation Guide
I use the official quick install script. Examples assume Ubuntu 22.04/24.04 as root.
Step 1: Prepare the Server
Update the system and install basic tools:
apt update && apt upgrade -y
apt install curl git wget jq openssl -y
Configure firewall (UFW example):
ufw allow OpenSSH
ufw allow 8000/tcp   # Coolify dashboard
ufw --force enable
Step 2: Run the Quick Installation (Recommended)
curl -fsSL https://cdn.coollabs.io/coolify/install.sh | sudo bash
Customize with environment variables (optional, run before the script):
env ROOT_USERNAME=admin \
ROOT_USER_EMAIL=admin@yourdomain.com \
ROOT_USER_PASSWORD=SuperSecurePass123! \
AUTOUPDATE=true \
bash -c 'curl -fsSL https://cdn.coollabs.io/coolify/install.sh | bash'
The installer:
- Installs Docker Engine (v24+).
- Sets up directories under
/data/coolify. - Configures SSH keys for server management.
- Starts Coolify services via Docker Compose.
Manual installation (for non-LTS or when the script fails):
-
Install Docker manually from official docs.
-
Create directories:
mkdir -p /data/coolify/{source,ssh,applications,databases,backups,services,proxy,webhooks-during-maintenance} mkdir -p /data/coolify/ssh/{keys,mux} mkdir -p /data/coolify/proxy/dynamic -
Generate SSH key:
ssh-keygen -f /data/coolify/ssh/keys/id.root@host.docker.internal -t ed25519 -N '' -C root@coolify cat /data/coolify/ssh/keys/id.root@host.docker.internal.pub >> ~/.ssh/authorized_keys chmod 600 ~/.ssh/authorized_keys -
Download files:
curl -fsSL https://cdn.coollabs.io/coolify/docker-compose.yml -o /data/coolify/source/docker-compose.yml # ... (other files: docker-compose.prod.yml, .env, upgrade.sh) -
Set permissions and start:
chown -R 9999:root /data/coolify && docker compose -f /data/coolify/source/docker-compose.prod.yml up -d.
Step 3: Access the Dashboard
After installation, I open http://YOUR_SERVER_IP:8000 and create the first admin account immediately (registration is open briefly).
Enable HTTPS (I do this before putting real apps on it):
- Coolify's built-in Let's Encrypt, or Traefik/Caddy as a one-click proxy inside Coolify.
Configuration
Coolify uses a .env file and Docker Compose for core settings. Mine lives at /data/coolify/source/.env.
Sample .env excerpt:
APP_NAME=Coolify
APP_ENV=production
APP_DEBUG=false
APP_URL=http://your-coolify-domain.com

DB_CONNECTION=pgsql
DB_HOST=postgres
DB_PORT=5432
DB_DATABASE=coolify
DB_USERNAME=coolify
DB_PASSWORD=your_secure_db_password

REDIS_HOST=redis
REDIS_PASSWORD=your_secure_redis_password

# Security
APP_KEY=base64:your_random_key_here
APP_ID=your_unique_app_id

# Advanced
PUSHER_APP_ID=...
PUSHER_APP_KEY=...
# etc.
What I actually change:
- Docker networks: address pool via install env vars if the default collides.
- Auto updates: on by default; I toggle it in settings once I have a backup habit.
- Resource limits: per project in the UI.
- SSH & servers: Coolify talks to servers with the SSH keys it generated. I add the host itself under Servers first.
Coolify runs its own PostgreSQL and Redis internally. For production apps I deploy dedicated databases as one-click services, not the Coolify DB.
When I deploy a Laravel app onto Coolify, I set APP_KEY, DB_CONNECTION, and the rest in that project's environment UI — those vars belong to the app, not to Coolify's own stack.
Usage: Deploying the first application
- Add a server (if I am not using the host): Dashboard → Servers → Add New (SSH details).
- Create a project: a folder for related resources.
- Deploy an application:
- Select Application → connect a Git repo (public/private with SSH key).
- Choose a build pack (Nixpacks auto-detects Laravel, Node, and others).
- Set build commands, start command, ports.
- Add environment variables and persistent volumes.
Example: deploy a Laravel app (this is the app I ship, not Coolify itself):
- Repo: my Laravel GitHub repo.
- Build pack: Nixpacks.
- Port: 80 or the app port.
- Env vars:
DB_HOSTpointing at a PostgreSQL service I deployed in Coolify. - Deploy: click Deploy and watch the logs.
One-click services:
- Databases, WordPress, Ghost, Vaultwarden — pick and deploy.
What I check after a deploy:
- CPU/RAM/disk in the UI.
- Logs and a shell inside the container.
- Scheduled backups once I have something worth restoring.
Testing:
- I deploy a static site or the official Coolify example first.
- Hit it via the assigned domain or IP:port.
- Confirm database links and that scheduled tasks actually run.
Screenshots and Visuals
The hero image is the architecture I care about: Coolify talks to Docker, apps sit behind Traefik, I only expose HTTPS.
Architecture: Coolify → Docker Compose/Swarm → apps/services → reverse proxy (Traefik) → internet.
Where it broke
On a fresh Ubuntu 24.04 box this install is famous for two walls. I hit the first one; the second shows up any time something else already claimed the dashboard port.
1. Snap Docker vs the installer
The script failed while bringing Docker up. The shape of the failure is "Docker is installed but Coolify cannot talk to the engine the way it expects." Official docs and Coolify's Discord keep repeating the same cause: Snap Docker.
Fix I used:
- Purge snap Docker.
- Install Docker Engine from Docker's apt repository (the installer can do this if snap is gone).
- Rerun:
curl -fsSL https://cdn.coollabs.io/coolify/install.sh | sudo bash
2. Port 8000 already in use
If another container or a leftover Coolify attempt is bound to 8000, the dashboard never comes up.
docker ps
I stop the conflicting container, then retry. Logs live under /data/coolify and docker logs coolify.
SSH failures after a manual install are usually ~/.ssh/authorized_keys missing the Coolify key, or permissions not 600. That is the next thing I check if the UI is up but "add this server" fails.
Troubleshooting
- Database connection errors on an app I deployed: env vars and service links in Coolify, not Coolify's own Postgres.
- Out of RAM:
htop, add swap, or move apps off the Coolify host. - HTTPS: DNS A/AAAA must point at this box; then read Let's Encrypt logs in the proxy.
- Updates stuck:
/data/coolify/source/upgrade.sh.
Community help: Coolify Discord.
Conclusion
Coolify is running on my VPS: dashboard on 8000 (HTTPS in front when DNS is ready), Docker Engine from the official repo, files under /data/coolify. I can git-push an app without opening a hosted PaaS tab.
Next I would lock SSH, put Uptime Kuma on the dashboard URL, and actually restore a backup once before I treat this as production. The Snap Docker fight is the part I wish I had known before the first curl | bash.
Did you hit the same wall?
I got stuck on Snap Docker blocking Coolify's installer. Did you hit the same thing, or a different one — port 8000 already taken, SSH keys that never landed in authorized_keys, HTTPS that would not issue? Tell me in the comments. I read them.
Need this done on your server?
I deploy and harden Laravel/CodeCanyon apps on cPanel or VPS, and offer monthly Server Watch retainers. Hire for deploy · Care plan