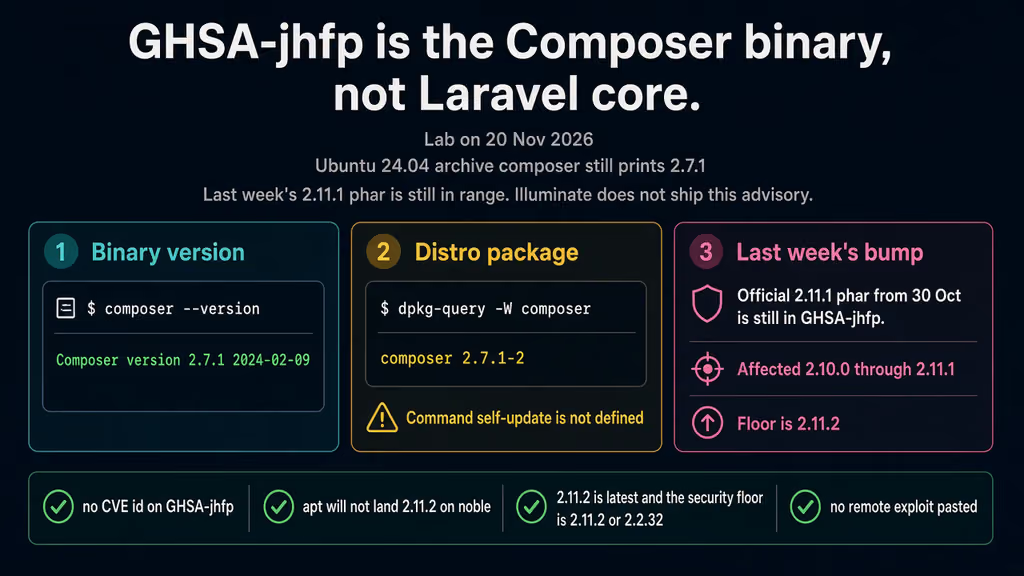
Caption: composer --version first. Last week's 2.11.1 bump is still in GHSA-jhfp. Illuminate does not ship this advisory.
I did not paste a crafted composer.lock at anything tonight. I opened Ubuntu 24.04.5 and installed archive php8.3-cli plus archive composer. php -v printed PHP 8.3.6, built 18 Nov 2026. PHP_VERSION_ID is 80306. Package 8.3.6-0ubuntu0.24.04.14. No php-fpm on this box. dpkg-query -W composer printed 2.7.1-2. composer --version printed Composer version 2.7.1 2024-02-09 15:26:28. Then:
Command "self-update" is not defined.
That is the same wall as 6 Nov. The new one sits on top of it. Two weeks ago I would have called a hash-checked 2.11.1 phar the floor. GHSA-jhfp-4ppm-crmm puts 2.11.0 and 2.11.1 back in range. --no-scripts does not close it. Lab note only. I did not write a remote exploit. I did not paste prevent_url_access_callable.
What changed
getcomposer.org dates the Composer 2.11.2 changelog to 11 Nov 2026. The download table dates the same tag to 10 Nov 2026. GitHub tagged it at 2026-11-10T09:24:59Z (12c820d). Same-day LTS: 2.2.32 at 2026-11-10T09:24:37Z. GHSA-jhfp-4ppm-crmm published 10 Nov 2026. Package: composer/composer, the tool. High (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H). CWE-78 and CWE-470. No CVE id. Debian tracks it as TEMP-0000000-AA2E99.
What I will treat as locked:
- Composer loaded
transport-options.prevent_url_access_callablefromcomposer.lock/vendor/composer/installed.json. A crafted lock or installed file madecomposer install/updaterun a system command while resolving downloads, before any checksum. No malicious package has to be installed.--no-scriptsand--no-pluginsdo not prevent it. A trusted local install from a lock nobody else can edit is out of scope. The realistic case is CI that runscomposer installwithout a human reading the lock diff. - Affected for GHSA-jhfp:
>= 2.10.0 < 2.11.2. Fixed in 2.11.2. 2.2 LTS never had that option handling. Ubuntu archive 2.7.1 is not in the jhfp range. Last week's 2.11.1 phar is. - 2.11.2 is still latest. Official phar sha256
dd158c0afd41d15fac89e1b4e47b5d42911fe316c3687cd5edac98319b25d028matched the download page (retrieved 20 Nov 2026). It printed Composer version 2.11.2 2026-11-10 10:09:37. I will not invent 2.11.3. - Ubuntu 24.04 archive Composer is still 2.7.1-2. Launchpad noble still lists that tag (uploaded 13 Feb 2024).
apt-cache policy: candidate 2.7.1-2, onlynoble/universe. I will not invent a USN. - Siblings, same tags. GHSA-w6hj-6587-3jh5 High: zip symlink write outside the package dir (
unzip→ZipArchivefallback). Affected>= 2.3.0 < 2.11.2and>= 1.0 < 2.2.32. Packagist.org-only installs are not a realistic vector. GHSA-x82q-x274-r6pq Moderate 6.5: inline repo HTTP credentials sent to lock-supplied dist mirrors — hits 2.11.0, 2.11.1, and 2.2.31. GHSA-6prc-h956-hxjq is the bundledsymfony/filesystemnote in the 2.11.1 phar (published 4 Nov 2026, no CVE). That is not a Laravel lock bump.
What I will treat as rumor: a Laravel-core CVE; composer audit as the check; --no-scripts as a workaround; the 12 Nov Packagist artifact-integrity post as this week's patch; 2.11.3 as a tag I can install.
What I would change in a real Laravel/PHP app this week
Three edits. None of them is composer update laravel/framework.
1. Prove the binary. Then prove it is a phar you can replace.
php -v
composer --version --no-ansi
which -a composer
file "$(command -v composer)"
dpkg-query -W -f='${Package} ${Version}\n' composer
apt-cache policy composer
composer self-update --dry-run
This lab printed:
PHP 8.3.6 (cli) (built: Nov 18 2026)
Composer version 2.7.1 2024-02-09 15:26:28
/usr/bin/composer: PHP script, ASCII text executable
composer 2.7.1-2
Command "self-update" is not defined.
composer diagnose warned Could not find Composer's installed.json — Debian split of the tool, not the project file in this advisory. which -a also printed /bin/composer (same wrapper, usr-merged).
2. Stop treating last week's floor as this week's floor.
function composerNov10SecurityFloorMet(string $version): bool
{
    if ($version === '') {
        return false;
    }
    // 2.2 LTS never had GHSA-jhfp. It still needs 2.2.32 for GHSA-w6hj / GHSA-x82q.
    if (str_starts_with($version, '2.2.')) {
        return version_compare($version, '2.2.32', '>=');
    }

    return version_compare($version, '2.11.2', '>=');
}

// Before — Ubuntu archive 2.7.1 fails. Last week's 2.11.1 fails GHSA-jhfp.
// composerNov10SecurityFloorMet('2.7.1');  // false
// composerNov10SecurityFloorMet('2.11.1'); // false
I ran that helper here. 2.7.1 → false. 2.10.3 → false. 2.11.0 / 2.11.1 → false. 2.2.6 / 2.2.31 → false. 2.11.2 / 2.2.32 → true. A jhfp-only check returns true for 2.7.1, because that tag was never in >= 2.10.0 < 2.11.2. That is not a pass. The deploy brake is the 10 Nov dump.
$out = [];
exec('composer --version --no-ansi 2>/dev/null', $out);
preg_match('/Composer version ([0-9]+\.[0-9]+\.[0-9]+)/', $out[0] ?? '', $m);
$version = $m[1] ?? '';
if (! composerNov10SecurityFloorMet($version)) {
    fwrite(STDERR, "Composer {$version} is below the 10 Nov 2026 Composer security floor.\n");
    exit(1);
}
That exit 1 is a deploy brake. The patch is the phar.
3. Install the official phar. Verify the hash. Put it ahead of /usr/bin/composer.
curl -fsSL -o composer.phar https://getcomposer.org/download/2.11.2/composer.phar
echo 'dd158c0afd41d15fac89e1b4e47b5d42911fe316c3687cd5edac98319b25d028  composer.phar' | sha256sum -c
sudo mv composer.phar /usr/local/bin/composer
sudo chmod +x /usr/local/bin/composer
hash -r
which -a composer
composer --version --no-ansi
On Ubuntu 22.04 archive (2.2.6-2ubuntu4), I would pin 2.2.32, not jump the major. LTS phar sha256 241a3d13b7c6d35d970b1f69a000298b66943541302148a438a932f5dd44a9fc. I would not paste a token.
What would bite on a self-hosted VPS
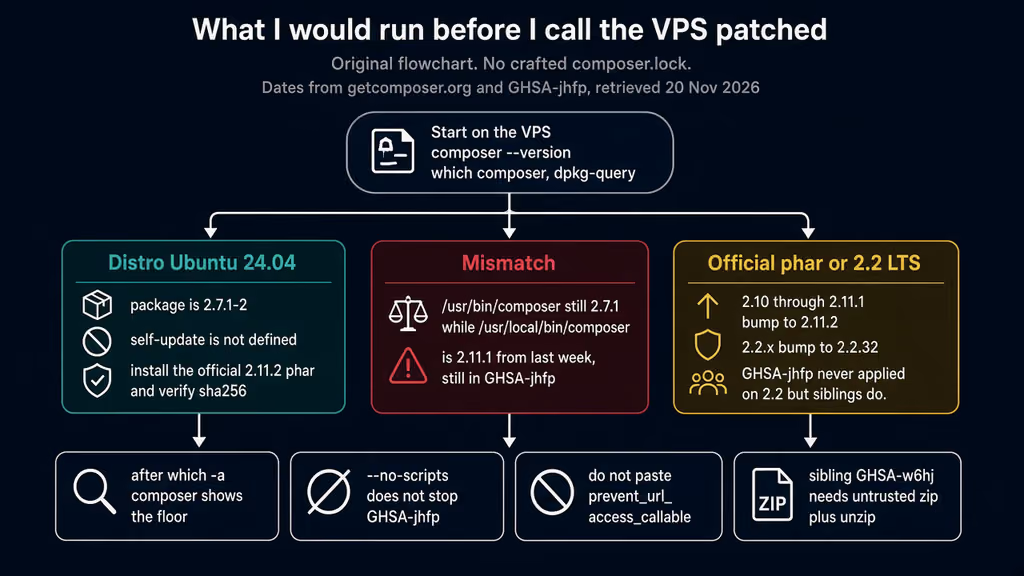
Caption: Distro 2.7.1-2 has no self-update. Last week's 2.11.1 phar is still in GHSA-jhfp. Official 2.11.2 phar, hash-checked. I did not paste a lock payload.
First bite: self-update is not defined. /usr/bin/composer on noble is a 3 KB wrapper that requires /usr/share/php/Composer/autoload.php. It is not a phar. apt upgrade composer stays on 2.7.1-2.
Second bite: last week's 2.11.1. I dropped that phar in /usr/local/bin on 6 Nov and told myself I was done. GHSA-jhfp starts at 2.10.0. 2.11.1 is the last vulnerable mainline tag. CI images from that post are the ones I would rebuild first. --no-scripts does not help — this is download-time callback handling from the lock, not a package script.
Third bite: PATH. I drop 2.11.2 into /usr/local/bin/composer and forget hash -r. The shell still runs /usr/bin/composer. which -a composer is the check. Shared hosting that will not replace /usr/bin/composer has no polyfill in app/. A trusted local composer install is the case the advisory calls not affected. An unreviewed lock PR is the case it names.
Ten days after the GitHub tag
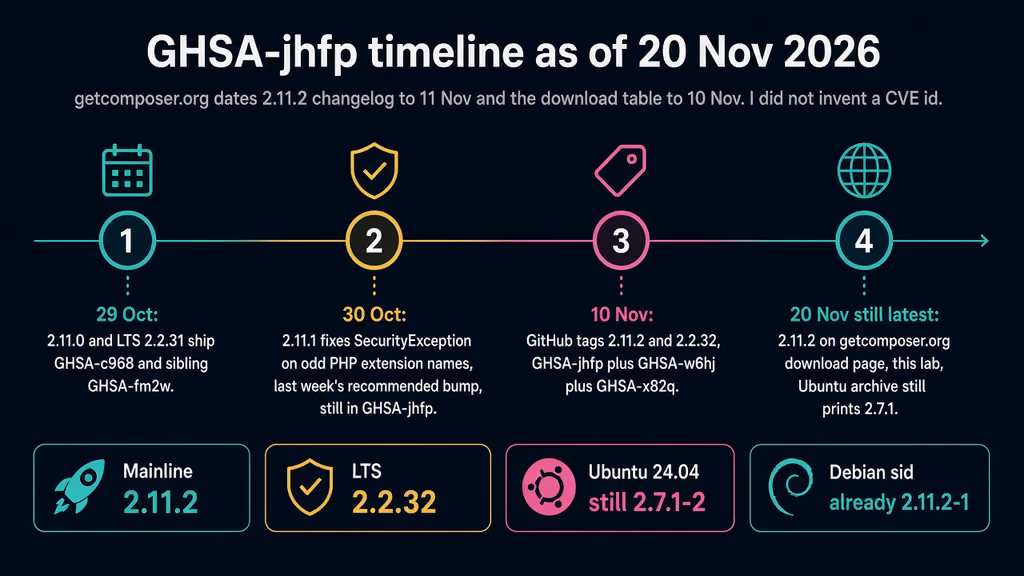
Caption: 2.11.0 and 2.2.31 on 29 Oct. 2.11.1 on 30 Oct. GitHub 2.11.2 and 2.2.32 on 10 Nov. I am writing 20 Nov. getcomposer.org still lists 2.11.2 as latest. Ubuntu 24.04 still prints 2.7.1. I did not invent a CVE id.
Debian sid and testing already have 2.11.2-1 (unstable 10 Nov 2026, testing 13 Nov 2026). bookworm and trixie are still listed vulnerable for TEMP-0000000-AA2E99. Honest target this week: Composer 2.11.2 as a hash-checked phar, CLI and CI the same binary. On 2.2 LTS: 2.2.32. I would not wait for noble to grow a USN. I would not invent 2.11.3 today. The PHP here is still 8.3.6 (.14 is a noble-security rebuild, changelog 19 Nov 2026 10:42 +1100). That is not this advisory.
Are you on this in production?
If composer --version already prints 2.11.2 (or 2.2.32 on LTS) on the same binary CI and the VPS use, you are on this. If it still prints 2.11.1 from the 6 Nov bump, you are not — that tag is in GHSA-jhfp. If Ubuntu 24.04 still shows 2.7.1-2, or which composer is /usr/bin/composer after a phar drop, you are not. If the laptop is 2.11.2 and the deploy image still apt install composer, you are not. Shared hosting that will not replace the distro wrapper is the last camp. I did not flip a client cluster tonight. I want to know which of those you are in.
Did you hit the same wall?
I would get stuck on Command "self-update" is not defined on Ubuntu archive Composer 2.7.1, or on a 2.11.1 phar I installed after GHSA-c968 and then treated as done. Did you hit the same thing, or a different one — PATH still pointing at /usr/bin/composer, a CI image frozen on 2.11.1, a host that will not let you replace the binary? Tell me in the comments. I read them.
If the blocker is the VPS itself (distro Composer, the wrong binary on PATH, a panel that will not let you install a phar), I do this class of bump for a living: Hire for deploy.
References
- Composer 2.11.2 changelog (2026-11-11): https://getcomposer.org/changelog/2.11.2
- GitHub Composer 2.11.2 (2026-11-10T09:24:59Z): https://github.com/composer/composer/releases/tag/2.11.2
- Composer 2.2.32 changelog (2026-11-10): https://getcomposer.org/changelog/2.2.32
- GitHub Composer 2.2.32 (2026-11-10T09:24:37Z): https://github.com/composer/composer/releases/tag/2.2.32
- GHSA-jhfp-4ppm-crmm (published 10 Nov 2026), High, no CVE id: https://github.com/composer/composer/security/advisories/GHSA-jhfp-4ppm-crmm
- GHSA-w6hj-6587-3jh5 (published 10 Nov 2026), High, no CVE id: https://github.com/composer/composer/security/advisories/GHSA-w6hj-6587-3jh5
- GHSA-x82q-x274-r6pq (published 10 Nov 2026), Moderate 6.5, no CVE id: https://github.com/composer/composer/security/advisories/GHSA-x82q-x274-r6pq
- GHSA-6prc-h956-hxjq, bundled
symfony/filesystemvuln present in the 2.11.1 phar (published 4 Nov 2026), no CVE id: https://github.com/symfony/symfony/security/advisories/GHSA-6prc-h956-hxjq - getcomposer.org download page (2.11.2 latest; sha256
dd158c0afd41d15fac89e1b4e47b5d42911fe316c3687cd5edac98319b25d028; 2.2.32 sha256241a3d13b7c6d35d970b1f69a000298b66943541302148a438a932f5dd44a9fc; retrieved 20 Nov 2026): https://getcomposer.org/download/ - Packagist blog, artifact integrity (12 Nov 2026) — not this patch: https://blog.packagist.com/artifact-integrity-for-packagist-and-composer/
- Launchpad Ubuntu noble composer 2.7.1-2 (uploaded 2024-02-13): https://launchpad.net/ubuntu/noble/+source/composer
- Launchpad Ubuntu jammy composer 2.2.6-2ubuntu4: https://launchpad.net/ubuntu/jammy/+source/composer
- Debian tracker, source package composer (sid/testing 2.11.2-1; TEMP-0000000-AA2E99; retrieved 20 Nov 2026): https://security-tracker.debian.org/tracker/source-package/composer
- Debian package tracker, composer 2.11.2-1 accepted unstable (2026-11-10), migrated to testing (2026-11-13): https://tracker.debian.org/pkg/composer
- Composer 2.11.1 changelog (2026-10-30), last week's bump, still in GHSA-jhfp: https://getcomposer.org/changelog/2.11.1
- GHSA-c968-33g3-wh7p (published 29 Oct 2026), the 6 Nov floor this tag replaces: https://github.com/composer/composer/security/advisories/GHSA-c968-33g3-wh7p